IT Asset Disposal Policy: What to Include and How to Enforce It
An IT asset disposal policy is a written rule set that says who retires a device, how its data is destroyed, who signs off, and what proof you keep. Write it before the first laptop leaves your building, because the data on a retired drive outlives the hardware. A policy that names the media types, the approved destruction method for each, a custody trail and a record you keep is the one that holds up with an auditor, an insurer or a patient.
If you run a small business or a medical practice, here is the uncomfortable truth: nobody attacks your network when an old copier or a dead server leaves the closet. They simply pick it up. This guide gives you the policy sections, the process and the evidence standard, with U.S. sources behind each one.
Table of Contents
TL;DR
- A disposal policy covers every device that might hold data: servers, laptops, phones, USB drives, backup media and printers, not only computers.
- Deleting files or formatting a drive is not sanitization. Use a method matched to the media type, following NIST SP 800-88 Rev. 2, published September 2025.
- Document every step: inventory entry, custody, method, certificate and final status. If it is not recorded, it did not happen.
- Healthcare practices must apply HIPAA safeguards to disposal, and HHS does not prescribe a single method, so your policy must show a risk-based choice.
- Disposal belongs to operations, security and vendor management together, not to one person in IT.
Table of Contents
- What an IT asset disposal policy actually is
- Which assets the policy must cover
- Data destruction rules: the core of the policy
- The disposal process, step by step
- Roles, approvals and records
- Healthcare and regulated businesses
- Mistakes that break a disposal policy
- A policy outline you can adopt
- Perspective
- Getting this running in your business
- FAQ
- Sources
What an IT asset disposal policy actually is
The FFIEC IT Examination Handbook, written for financial institutions but a useful model for any small business, describes the expected control as a written policy, standard and procedure for disposing of or transferring physical media such as paper, electronic media such as hard drives, disks and removable drives, virtualized copies, and equipment such as printers.
Three words in that description matter for you.
- Policy states the rule: no device leaves company control until its data is sanitized or destroyed and the result is recorded.
- Standard names the technical bar, for example which sanitization method applies to which media.
- Procedure lists the steps and who performs them.
Most small businesses have none of the three. They have a closet of old equipment and a vague plan to deal with it someday. That closet is a liability you are paying to store.
The same FFIEC guidance says disposal controls should be risk-based, scaled to the sensitivity of the information and the type of media. A drive from a reception desktop and a drive from your accounting server do not carry the same risk, and your policy should say so.
Which assets the policy must cover
Start with the obvious hardware, then go looking for what people forget. The UK’s National Cyber Security Centre advises treating every device that might contain electronic storage media as potentially data-bearing. That is a sound rule for any country.
Your scope list should include:
- Desktops, laptops and tablets.
- Servers, including virtual machine copies and any storage attached to them.
- Phones, including personal phones that hold company email.
- External drives, USB sticks and other removable media. We cover the exposure in our piece on the risks of removable media.
- Backup tapes and disks.
- Network gear whose configuration holds credentials.
- Printers and multifunction copiers. FFIEC specifically tells management to address equipment such as printers that may retain residual data, and our write-up on printer security risks shows why those devices are so often missed.
- Paper that carries sensitive information.
If you cannot list your assets, you cannot dispose of them safely. A working inventory is the foundation, and our IT asset management roadmap walks through building one for a small company.
Data destruction rules: the core of the policy
This is the section readers searching for a data destruction policy came for, and it is where most weak policies fail. They say “wipe the drive.” That is not a standard.
Deletion and formatting are not enough
The NCSC guidance is direct: a policy should not assume ordinary deletion or formatting is sufficient, and storage media should be sanitized before it leaves organizational control. Files you delete are often still recoverable, because the operating system only removes the pointer to them.
Use the three NIST outcomes
NIST SP 800-88 Rev. 2, the federal media sanitization guideline published in September 2025, supersedes Rev. 1 and helps an organization build a sanitization program around the sensitivity of its information. It keeps three outcomes:
| Outcome | What it means | Media can be reused? |
|---|---|---|
| Clear | Protects against simple, non-invasive recovery attempts | Yes |
| Purge | Makes recovery infeasible even with state-of-the-art laboratory techniques | Often yes |
| Destroy | Makes recovery infeasible and leaves the media unusable | No |
Your policy should assign an outcome to each data classification. Low-sensitivity media might only need Clear. Drives that held client financial records or patient data should get Purge or Destroy.
Match the method to the media
FFIEC notes that degaussing, which uses a strong magnetic field, is not effective on flash media such as SSDs and USB drives. Methods must be selected by media technology, never applied uniformly. A policy that says “degauss everything” fails on every modern laptop.
A practical method table for your policy:
| Media | Typical approach |
|---|---|
| Hard disk drives, reusable | Certified erasure to a recognized standard, then verify |
| SSDs and USB flash | Erasure methods built for flash, or physical destruction; not degaussing |
| Drives that cannot be erased or are failed | Physical destruction |
| Backup tapes | Destruction or purge per the data classification |
| Paper | Shredding |
Verify and document the result
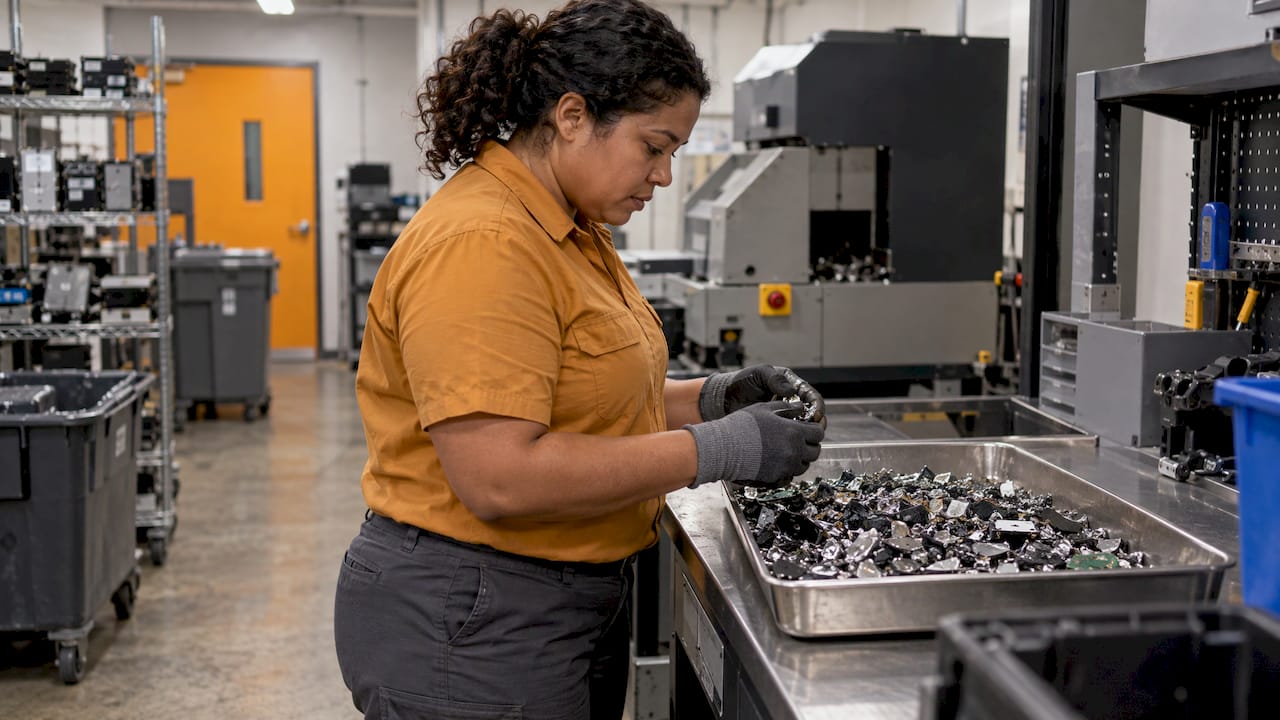
NIST’s guideline points to a certificate for each unit confirming sanitization or destruction. For physical destruction, the NCSC says to use an appropriate method and document inspection of the remnants. For certain scenarios it specifies particles of 6 millimeters or less and says the particle size should be verified. Whoever signs off should look at the output, not just trust a receipt.
The disposal process, step by step
A policy is only as good as the routine behind it. This sequence works for a business of 10 or 200 people.
- Flag the asset. Decide the device has reached end of life, and mark it so nobody reuses or sells it informally.
- Inventory it. Confirm ownership and record serial number, type, location and the sensitivity of the data it held. This is the step that tells you which sanitization outcome applies.
- Assign roles and a timeline. Name who approves, who performs, and how many days a flagged device may sit before it is processed. Devices parked indefinitely in a supply closet are the usual source of loss.
- Retrieve it securely. The NCSC advises that assets marked for disposal be securely retrieved with chain of custody documented from the collection point to the staging area. Lock the staging area and log who has the key.
- Sanitize or destroy. Apply the method your standard assigns to that media and classification.
- Verify. Confirm the erasure report or inspect the destroyed remnants.
- Choose the end route. After sanitization, equipment can be resold, returned to a lease provider, donated if still functional, or sent to a certified electronics recycler. The sanitization step comes first, always.
- Collect the certificate and close the record. Update the inventory so the asset shows its final status, with the certificate and any receipts attached to its entry.
Where most small businesses go wrong is step 3 and step 8. Nobody owns the timeline, and nobody closes the record, so six months later there is no proof either way.
Roles, approvals and records
FFIEC treats disposal as a shared responsibility among operations, information security and third-party service-provider management, not an IT-only task. For a small company, translate that into three named roles:
- The owner or administrator approves the policy and signs off on exceptions.
- Whoever manages IT executes sanitization and keeps the inventory current.
- Whoever handles vendors vets any outside party that takes custody of equipment.
In a ten-person firm one person may hold two of those roles. That is fine. What matters is that every asset has a named person responsible at each stage.
For records, a health system’s published equipment disposal policy is a good model of the level of detail: defined roles, approved methods, documented custody, vendor vetting against recognized certifications and contract terms, and certificates attached to each asset record. That policy retains certificates of disposal for a minimum of six years. Set your own retention period with your attorney or compliance adviser, and write it into the policy.
What to require from an outside disposal vendor
If an outside company takes your equipment, the policy should require:
- Recognized industry certifications, which you check rather than accept on a brochure.
- A contract that states the destruction method, custody handling and liability.
- A certificate for each unit, tied to its serial number.
- A right to receive records for your files.
The vendor is an extension of your own control. If their process fails, your data is the data exposed.
Healthcare and regulated businesses
If you handle patient information, disposal is a compliance matter, not a housekeeping one. The HHS Office for Civil Rights explains that the HIPAA Privacy Rule requires reasonable administrative, technical and physical safeguards for PHI during disposal. The Security Rule goes further for electronic PHI: policies for the final disposition of ePHI and of the hardware or media it is stored on, plus procedures for removing ePHI before media are reused.
Two points follow for your policy.
- HHS says HIPAA does not mandate a single disposal method. Covered entities must assess risk based on the form, type and amount of PHI and implement reasonable safeguards. Your policy should therefore record why each method was chosen for each media class.
- Reuse is covered too. A laptop handed from the front desk to a new hire is a disposal event for any ePHI on it.
For related practical guidance, see our posts on meeting HIPAA compliance with a managed IT plan and becoming a HIPAA compliant facility. If you hold customer financial data, the same logic applies: sanitize before anything leaves your control, and keep the record.
Mistakes that break a disposal policy
- Writing the policy and never inventorying. You cannot sanitize a device you do not know exists.
- Treating all media the same. One method for everything guarantees it is wrong for something.
- Forgetting printers, phones and removable drives. These carry data and rarely appear on the equipment list.
- Donating before wiping. The good deed becomes a breach.
- Accepting a receipt as proof. A certificate needs a serial number that matches your inventory.
- No exception process. When a failed drive cannot be wiped, the policy should say it is destroyed, and say who approves.
These gaps are the same ones behind many of the failures we describe in five costly small business security mistakes. Disposal is a security control like any other, and it deserves the same scrutiny as your firewall.
A policy outline you can adopt
Use this skeleton as your first draft and fill it in with your own roles and methods.
- Purpose and scope: what the policy protects and which assets it covers.
- Definitions: data-bearing device, sanitization, Clear, Purge, Destroy.
- Classification link: which data sensitivity maps to which outcome.
- Approved methods by media type.
- Roles and approvals.
- Custody and staging rules.
- Vendor requirements.
- Records and retention: certificates, inventory status, retention period.
- Exceptions and incidents: what happens if a device goes missing.
- Review schedule: revisit at least annually and whenever a standard changes, as NIST did in 2025.
Perspective
We see disposal as the last chapter of the security lifecycle, and it is the chapter most businesses skip. A firewall policy gets reviewed every year. A retired server sits in a closet for three.
Our view is that disposal belongs inside your ongoing IT management, not beside it. The inventory that tells you what you own is the same inventory that tells you what must be wiped. The risk assessment that tells you which data matters is the same one that decides whether a drive is cleared or destroyed. When those pieces are connected, a disposal policy is a short document you actually follow. When they are separate, it becomes a PDF nobody opens.
If you run a small business or a healthcare practice, the weak link is rarely the exotic attack. It is the unlogged device walking out the door. Close that gap with a written standard, a named owner and a record for every unit.
Randy Bryan
Getting this running in your business
A policy needs an owner, an inventory and a risk-based view of your data. tekRESCUE provides managed IT services for small and midsize businesses in Austin, San Marcos and the surrounding Hays County area, along with cybersecurity services and risk assessment and HIPAA compliance support. If you want a disposal policy that fits your equipment and your regulatory obligations, contact us and we will start from your asset list.
FAQ
What is the most secure way to dispose of an old device?
Sanitize it to a recognized standard before it leaves your control, and destroy it physically if it cannot be reused or your policy requires it. Choose the method by media type, since degaussing does not work on flash storage. Keep a certificate for each unit.
Is deleting files or factory resetting enough?
No. The NCSC advises that ordinary deletion or formatting should not be assumed sufficient. Use a sanitization method assigned by your policy and verify the result before the device is resold, donated or recycled.
How long should I keep disposal records?
HIPAA and other rules do not set one number for every business, so set the period with your compliance adviser or attorney. One published health system policy keeps certificates of disposal for at least six years, which shows the scale regulated organizations plan for.
Does HIPAA require a specific data destruction method?
HHS says it does not. You must assess risk based on the form, type and amount of PHI and apply reasonable safeguards. Your policy should document why you chose each method for each media type.
Do printers and copiers need to be in the policy?
Yes. FFIEC tells institutions to address equipment such as printers that may retain residual data. Treat them as data-bearing devices, list them in your inventory and sanitize them before return or disposal.
Sources
- FFIEC IT Examination Handbook: Disposal of Data and Media
- NIST SP 800-88 Rev. 2, Guidelines for Media Sanitization
- NCSC: Secure sanitisation and disposal of storage media
- NCSC: Decommissioning assets
- Northwell: 900.29 Equipment Disposal Policy and Procedure
- HHS OCR: FAQs About the Disposal of Protected Health Information
Recommended
Table of Contents