Small Business Cybersecurity Reality: Avoid These Five Costly Mistakes
Small operations face the exact same digital threats as international corporations. Bad actors use automated tools to scan thousands of IP addresses every minute, looking for open ports, outdated software, and weak passwords. They do not check company revenue before launching an attack. When a system drops offline, the damage hits a small team much faster and harder than a large enterprise with massive reserves.
Recovery costs extend far beyond paying a ransom or buying new computers. Operational downtime halts billable work, customer data leaks destroy market reputation, and legal compliance fines accumulate quickly. Most small business owners assume their IT setup handles basic protection, but minor oversights leave huge doors open for network entry. Fixing these operational gaps costs a fraction of what a real incident response process demands.
Small Business Security Checkpoints
- Endpoint: Replace standard antivirus with EDR software.
- Patching: Auto-update OS and apps within 7 days.
- Authentication: Require MFA via authenticator apps across all logins.
- Backups: Use 3-2-1 rule with isolated, immutable cloud vaults.
- Management: Hand off daily log reviews and monitoring to specialists.
Table of Contents
Mistake 1: Relying Solely on Built-In Antivirus Software
Basic endpoint security that comes pre-installed on desktop operating systems provides a foundational layer of protection. However, native tools rely primarily on known signature databases. Modern threats use custom code, fileless malware, and script-based execution paths that bypass signature scanning entirely.
When an employee opens a malicious email attachment or visits a compromised website, default tools often miss the initial execution phase. Advanced detection requires behavioral analysis that monitors how applications interact with local memory and network drivers. Without endpoint detection and response solutions, bad actors gain silent access and stay inside a network for months.
How to Fix It
Replace standard desktop software with managed Endpoint Detection and Response tools. These programs continuously monitor system memory, process execution, and outgoing network connections to block suspicious activity before it spreads.
Mistake 2: Delaying Operating System and Application Updates
Software updates do far more than add new user interface features. Developers release security patches to close known system vulnerabilities that hackers actively exploit. When a vendor publishes a patch, bad actors reverse-engineer the code to find the exact weakness and create targeted exploits.
Unpatched software gives network intruders a direct, predictable way inside your network. Postponing updates for weeks or months leaves every connected workstation vulnerable to automated scanning tools. Leaving third-party applications like web browsers, PDF readers, and accounting tools outdated creates identical risk vectors.
How to Fix It
Enable automatic updates across all operating systems and third-party software applications. Set up a centralized patch management service to verify that every device on your network receives updates within seven days of release.
Mistake 3: Skipping Multi-Factor Authentication on Business Email
Password reuse remains a primary entry method for account takeovers. Employees frequently use identical or slightly modified passwords across personal and work accounts. When a third-party website suffers a data breach, hackers take those credentials and run them against business email platforms.
A compromised email account grants full access to internal conversations, vendor invoicing details, and client lists. Intruders impersonate executives to authorize fraudulent wire transfers or send phishing links directly to your customers. Single-factor password protection is no longer sufficient to secure business communication.
How to Fix It
Require multi-factor authentication across all business email logins, cloud storage accounts, and remote access portals. Use authenticator applications or physical security keys rather than text-message codes, which remain vulnerable to SIM-swapping attacks.
Mistake 4: Storing Backups on the Same Network
Having a backup system does not guarantee business recovery if those files sit on the same local network as primary servers. Modern ransomware strains explicitly target connected backup drives, network-attached storage units, and active cloud sync folders before encrypting primary file systems.
If your backup drive stays plugged into a server overnight, ransomware will encrypt the backup right along with the operational data. This leaves management with zero clean restoration points, forcing prolonged operational downtime or complete data loss. True data resilience requires physical and logical isolation.
How to Fix It
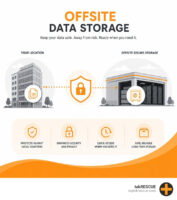
Implement a strict 3-2-1 backup strategy: keep three copies of your data on two different media types, with one copy stored offsite in an immutable cloud vault that prevents file modification or deletion.
Mistake 5: Treating Cybersecurity as an Internal DIY Project
Managing network defenses requires dedicated tools, constant monitoring, and specialized training. When small business owners assign IT security to an internal office manager or a single generalist employee, critical maintenance items slip through the cracks.
Internal staff often lack the time to review daily log files, analyze threat intelligence reports, or test backup restoration reliability. True network defense requires proactive maintenance, continuous monitoring, and structured incident response planning. Handling security as a part-time chore creates a false sense of safety until an actual breach occurs.
How to Fix It
Partner with a dedicated managed service provider to handle round-the-clock monitoring, patch validation, and network security management. Professional oversight frees your team to focus entirely on running daily operations.
FAQs
What is the single most effective security step a small business can take today?
Enforcing multi-factor authentication across every email account and cloud application delivers the highest immediate protection against unauthorized network entry.
How often should a small business test its data backups?
Run a full backup restoration test at least once every quarter to confirm that files restore cleanly without corruption or missing directory structures.
Why is text-message verification less secure than an authenticator app?
Text messages travel through unencrypted cellular networks that hackers can intercept or redirect through SIM-swapping attacks, whereas authenticator apps generate secure codes directly on your local device.
Does cyber insurance replace the need for active security software?
No, insurance carriers require policyholders to maintain specific security controls like multi-factor authentication and managed backups before paying out any claims related to a breach.
How much downtime should a business expect after a ransomware incident?
Without immutable backups and a structured incident response plan, average business recovery takes anywhere from 10 to 21 days of total operational paralysis.
Protect Your Network with Practical Defense Controls
Securing a business network does not require millions of dollars in enterprise software, but it does demand consistent operational discipline. Eliminating weak passwords, patching software promptly, securing isolated backups, and turning on multi-factor authentication creates a strong defense that stops the vast majority of automated attacks.
Taking a structured approach protects your revenue, preserves client trust, and keeps daily operations running smoothly. Review your current technology setup today to identify where gaps exist. To see how dedicated technical management keeps your business secure, reach out to the team at tekRESCUE.
Table of Contents